Cloud Computing for Law Firms: Hosting, Security, and ROI
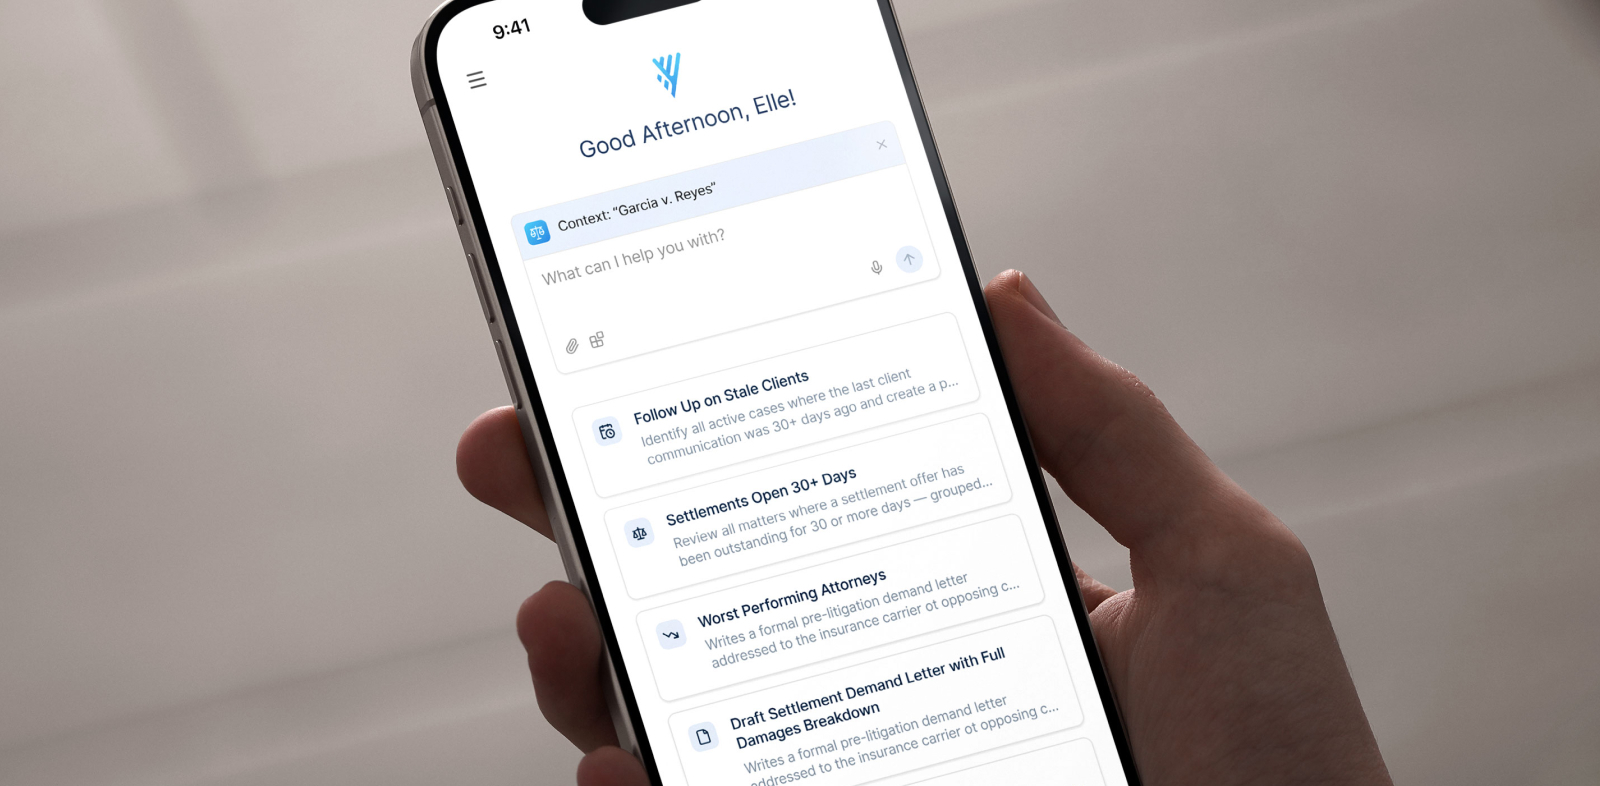
Cloud computing for law firms involves storing case files, documents, and practice management software on infrastructure maintained by a cloud provider, accessed through a browser rather than a server in your office. Most firms have already made the shift: 73% now use cloud-based legal tools, according to the American Bar Association. Litify is a cloud-based legal operations platform that leverages the power of the Salesforce platform to give firms browser-based access to matters, documents, and reporting without the overhead of maintaining their own hardware. In this blog, we’re discussing everything firms should know about on-premise server solutions and cloud computing, including the limitations of server-based access, what cloud computing looks like in practice, and how to overcome resistance to a cloud-based approach.
Law firms are under increasing pressure to manage growing volumes of sensitive data, respond to clients faster, and stay ahead of rising cybersecurity threats. Many still rely on on-premise IT systems that are expensive to maintain and difficult to scale.
Cloud computing in the legal industry is no longer an experiment, and the debate about whether the cloud belongs in legal work has largely settled.
What remains unsettled for law firms is the sequencing: which systems to move, when to move them, and whom to trust with their data. This guide covers how on-premise systems fall short, what cloud hosting for law firms actually involves, what firms gain, and how to evaluate a provider before you sign.
Why on-premise IT is failing law firms
On-premise setups offer a sense of control, but that control is getting harder to justify financially and operationally.
Costly maintenance
Owning your IT infrastructure means owning a long list of recurring obligations. You pay for the equipment, the space to house it, the environmental controls to protect it, and the people to keep it running.
Those costs are not one-time. Servers have a set lifespan, licenses renew, and every new case, client, or hire adds load to a system that only expands when you buy more storage space.
Security risks
In-house systems fall behind quietly. Threats change faster than most firms can staff against, and without dedicated security resources, a missed patch or a forgotten access point can go unnoticed for months.
IBM's 2026 Cost of a Data Breach Report found that only 37% of breached organizations encrypt sensitive data both at rest and in transit. That is the single most fundamental control available, and most organizations that have dealt with a breach were not consistently encrypting their data. The same report put the global average cost of a breach at a record $4.99 million, with the US average at $11.5 million.
Operational inflexibility
Hybrid work has become more normalized across the industry, and most on-premise systems were not designed for it. Remote access to on-premises systems typically relies on workarounds, and increasing headcount or scaling the number of people working off-site can often lead to downtime while those updates are made.
What cloud hosting for law firms actually means
Cloud hosting for law firms means a provider owns and operates the servers, storage, and network your software runs on, and your team reaches that software over the internet.
The National Institute of Standards and Technology (NIST) provides the standard definition, including five essential characteristics of any cloud service:
- On-demand self-service: You can add users or capacity without a purchase order and a technician visit.
- Broad network access: The service works over standard connections from laptops, tablets, and phones.
- Resource pooling: The provider serves many customers from shared infrastructure.
- Rapid elasticity: Capacity expands and contracts with your caseload.
- Measured service: Usage is metered, so you pay for what you consume.
NIST also separates cloud computing into three service models:
- Software as a service (SaaS) delivers a finished application
- Platform as a service (PaaS) delivers a development environment
- Infrastructure as a service (IaaS) delivers raw computing power
Nearly all who are buying cloud software for law firms are buying SaaS, where the provider handles everything beneath the application.
The deployment model is the choice that actually affects your firm:
- Public cloud, or multi-tenant SaaS: Shared infrastructure operated by the vendor, with each customer's data logically separated. This fits most firms most of the time, because it carries the lowest overhead and the fastest path to current security controls.
- Private cloud for law firms: A dedicated environment reserved for one organization. Private deployments are usually driven by a specific client mandate or a regulatory requirement rather than by a security need the public cloud cannot meet. This strategy costs more and updates more slowly.
- Hybrid: Some systems stay local while others move to a hosted environment. Hybrid is common, but it is more often a stage in a migration rather than a permanent destination.
Corporate legal departments weighing the same tradeoffs for enterprise legal management face a nearly identical decision, with the added variable of how the department's systems connect to the rest of the business.
Comparing cloud vs. hybrid deployment models for legal practice management
Cloud and hybrid deployment differ in where accountability sits. In a fully cloud-hosted model, one provider is responsible for the infrastructure, the security patching, and the uptime commitment. In a hybrid model, your firm keeps part of that responsibility and takes on the work of connecting two environments that were not designed together.
That connective work is the hidden cost. Hybrid setups require someone to own identity management across both sides, keep security standards aligned, and troubleshoot problems that could originate in either place. Firms that deliberately adopt a hybrid approach with a defined endpoint generally do well. Firms that drift into the hybrid model because they’re moving one system at a time without a plan end up bearing two sets of costs indefinitely.
The case for moving to the cloud
Firms that move to cloud services tend to cite five main benefits:
Cost and scale
Cloud platforms convert capital expense into operating expense. There are no servers to buy, no refresh cycle to budget for, and no hardware to replace when it fails.
Scale follows the same logic. Adding attorneys, opening an office, or absorbing a larger caseload becomes a licensing and configuration change rather than an infrastructure project. Firms with uneven growth benefit most because they stop paying year-round for capacity they need in bursts.
Security and compliance
Law firms and cloud security are more compatible than their reputation suggests, because established providers apply controls that most firms cannot staff on their own. That typically includes encryption at rest and in transit, multi-factor authentication, continuous monitoring, and independent audits against recognized frameworks such as SOC 2.
Cloud platforms maintain layered backups across separate locations, so a hardware failure, a ransomware incident, or an accidental deletion does not render case data inaccessible.
Firms handling medical records, financial data, or other regulated material are routinely asked how that information is protected, and a documented answer is easier to provide when your software supports audit trails.
Access from anywhere
Attorneys and clients now expect around-the-clock access to case information. Server-based access strategies struggle here. Virtual private networks are slow and add friction to routine work. Emailing documents to yourself is not an access strategy at all, since it creates duplicate work and risks someone drafting from a stale version.
With a cloud platform, attorneys and staff review documents, exhibits, and client information from the office, from home, from a courthouse, or while traveling, on whatever device is in front of them. Everyone works from the current version because there is only one source of truth.
Less to maintain
Updates arrive automatically. The provider applies security patches, feature releases, and compliance changes without a maintenance window that your team has to schedule and staff.
Integrations get easier, too. Once your core system is cloud-based, connecting it to the other tools your firm already uses is a supported configuration rather than a custom project.
There is less to maintain on the environmental side, as well. Shared data centers run more efficiently than a room of underused servers, which reduces both energy use and your utility bill.
Room to adopt what comes next
A cloud foundation determines what your firm can adopt later. Analytics, document automation, and legal AI tools are built to connect to cloud platforms, and firms on legacy systems often find that the integration cost exceeds the value of the tool itself.
More and more firms are making the migration, too, so those sticking with on-premise solutions risk falling behind. The International Legal Technology Association's 2025 Technology Survey, which gathered input from 580 firms representing more than 152,000 attorneys, found that firm infrastructure is steadily moving to the cloud, with cloud and virtual server deployments rising as traditional hardware purchases decline.
Debunking cloud myths
When evaluating legal cloud-based software solutions, these core objections should be addressed:
"The cloud isn't secure."
Cloud platforms can securely store confidential client data, and the industry’s own ethics bodies have confirmed this. Every state bar that has issued an ethics opinion on whether lawyers may use cloud-based platforms has permitted it, subject to a reasonable-care standard requiring the lawyer to perform appropriate due diligence on the provider.
ABA Formal Opinion 477R also concludes that cloud-based software can handle the electronic transmission of client information.
To address this, it’s important to be precise about how cloud security actually works. Responsibility is shared: the provider secures the infrastructure, and your firm secures what it puts on top of that foundation, including user accounts, permissions, and access habits. Most breach incidents trace to issues with permissions and access rather than to a failure of the platform, which is why multi-factor authentication is crucial.
"Migration is too disruptive."
Migration does not require flipping a switch overnight. Most firms move in phases, starting with lower-risk systems and shifting core matter data once the team is comfortable with the environment.
A phased plan also gives you checkpoints. If something needs adjusting, you find out during a limited rollout rather than after your entire practice depends on it. Ask any provider you evaluate to describe the phases they recommend and what they handle at each one.
"We'd lose control of our data."
Your firm owns its data within a properly structured cloud arrangement, and the vendor contract should state this clearly. Control comes down to three things you can verify before signing: ownership language in the agreement, a documented export path that returns your data in a usable format, and audit trails that record who accessed what and when.
Audit logging is often the most valuable. A cloud platform can show you every login and every record a user touches, which is visibility that most on-premise setups cannot produce without additional tooling. You can review the data security practices we apply as one example of what that documentation should look like.
How to evaluate a cloud provider
Cloud solutions for law firms vary, so treat these items as a guide rather than set-in-stone criteria. Each consideration produces a document or a commitment that you can file, which is the practical form your due diligence should take.
1. Confirm the compliance posture
Ask for a current SOC 2 Type 2 report. Type 2 matters because it examines whether controls actually operated over a period of time, usually six to twelve months, rather than whether they existed on a single day. Request one issued within the last twelve months.
Confirm that data is encrypted both at rest and in transit, since that combination is far from universal. And if your practice touches medical records, which covers most personal injury and mass tort work, understand that a provider handling that data is a business associate under HIPAA and needs a signed business associate agreement. The Department of Health and Human Services has been explicit that this applies even when the data is encrypted, and the provider cannot read it, and that a service-level agreement does not substitute for the agreement itself.
2. Ask how migration is phased
Have the provider walk you through a specific sequence, not a general philosophy. You want to know which systems move first, how long each phase runs, who performs the data mapping, and what happens to historical matters.
Ask what a comparable firm's timeline looked like. A provider who has done this repeatedly will respond with weeks and dependencies rather than reassurances.
3. Check what training and implementation support is included
Find out what is in the contract and what costs extra. Good technology delivers nothing if your team does not know how to use it, and adoption problems are the most common reason a sound platform underperforms.
Ask who trains your staff, whether training is role-specific, and what support looks like after go-live. Litify provides training and implementation support as part of the engagement, ensuring teams work confidently before the old system is retired.
4. Understand uptime commitments and recovery targets
Get the numbers in writing. Ask for the contractual uptime commitment, how the provider measures it, and what remedy applies if it is missed.
Then ask two questions: how quickly can service be restored after an outage, and how much recent work could be lost. Providers track these as recovery time and recovery point objectives, and vague answers here are a meaningful signal.
5. Verify your data stays exportable
Confirm in writing that you can retrieve your data in a usable format at any point, including at the end of the relationship. Ask what formats are supported, how long an export takes, and how long the provider retains your data after termination.
Exportability is the practical test of ownership. A provider confident in its product will not make leaving difficult.
How Litify supports cloud-based legal work
Litify is a cloud-based legal operations platform built for law firms and legal departments, and it leverages the power of the Salesforce platform to offer:
- Browser-based access from any device: Attorneys and staff log in securely from the office, home, or the courthouse and pick up where they left off.
- Enterprise-grade security is built in: The infrastructure includes encryption, multi-factor authentication, and access controls applied by default.
- Phased migration support: Firms move in stages, with mapping and validation handled alongside the Litify team rather than by internal staff alone.
- Training during implementation: Teams learn the system before it becomes the system of record.
- Configurable rather than rigid: Firms can adjust intake, matter workflows, and reporting to how they actually operate instead of reshaping their practice around fixed software.
You can see how these pieces fit together across the Litify platform.
Timing your firm's move to the cloud
The decision facing most firms considering cloud-based solutions is one of timing, not direction. The industry has already moved; the ethical questions have been answered; and the tools that will matter over the next several years are being built to run on cloud infrastructure. What remains is choosing a sequence that fits your caseload, your calendar, and your tolerance for change, then choosing a provider who can best support your firm during the transition and beyond.
Request a demo to see how Litify supports secure, cloud-based legal work.
Frequently asked questions
Is cloud computing secure enough for law firms?
Yes. Every state bar that has issued an ethics opinion on cloud use permits it, provided the lawyer performs reasonable due diligence on the provider. Established cloud platforms apply encryption, multi-factor authentication, and independent audits that most firms cannot maintain internally.
What is the difference between cloud hosting and cloud storage for a law firm?
Cloud storage holds and syncs documents. Cloud hosting runs the applications your firm uses, such as intake, matter management, and reporting. A firm can have solid document storage and still run its practice on an aging server, which is why storage alone rarely produces the efficiency gains firms expect.
How long does it take a law firm to migrate to the cloud?
Most migrations run in phases over several weeks to several months, depending on data volume, the number of systems involved, and the amount of historical data being moved. Litify structures migrations in stages so firms keep working throughout rather than pausing operations for a single cutover.
What should legal teams consider when migrating to cloud-based legal software?
Focus on four things: which systems move in which order, who performs the data mapping and validation, what training your team receives before go-live, and what your export rights look like afterward. Getting the sequence and the training right prevents most of the problems firms attribute to the software itself.
Which cloud legal platforms offer the strongest security and compliance controls?
Compare providers on documentation rather than claims. Ask each for a SOC 2 Type 2 report issued within the last twelve months, confirmation that data is encrypted at rest and in transit, and a business associate agreement if your practice handles medical records. Litify leverages the power of the Salesforce platform, which carries the compliance certifications expected in regulated industries.
Which cloud-based legal platforms provide the best uptime and disaster recovery?
Judge this on contractual commitments, not marketing language. Ask for the stated uptime commitment, how it is measured, what remedy applies if it is missed, and the provider's recovery time and recovery point targets. Providers with mature recovery programs answer these with specific numbers and can describe their backup locations.
What are the benefits of cloud computing for law firms?
The main benefits are lower and more predictable IT costs, security controls maintained by specialists, access from any device, automatic updates, and a foundation that supports newer tools such as analytics and legal AI. Firms also gain easier scaling, since adding users becomes a configuration change rather than a hardware purchase.
Is cloud-based legal practice management more secure than on-premises software?
Usually, but not automatically. A reputable cloud provider applies encryption, monitoring, and audited controls at a level most firms cannot match internally. Security in the cloud is shared, though, so the provider secures the infrastructure while your firm remains responsible for user accounts, permissions, and access practices.
Additional Sources
American Bar Association, 2024 Legal Technology Survey Report | American Bar Association, Cloud Ethics Opinions Around the U.S. | National Institute of Standards and Technology, Cybersecurity Framework 2.0 Cybersecurity and Infrastructure Security Agency, Cloud Security